NEW Wi-Fi 7 지원 엔터프라이즈급 WBE630S AP 출시  자세히 보기 →
제품 / 자료 검색

USG FLEX H Series

USG FLEX 200H

USG FLEX H Firewall

  • 중견 규모 비즈니스를 위한 올인원통합 방화벽 기능
  • 관리플랫폼 간 스마트 동기화
    • 로컬 & 클라우드 동시 관리
  • 멀티 기가 포트 제공
    • 최대 10GbE(FLEX 700H) 제공
  • 802.3at PoE+ 포트 제공
    • FLEX 500H/700H 2개 포트 제공
  • 라이선스 기반의 통합보안장비
    Gold Security Pack / Entry Defense Pack
    • Sandboxing
    • Reputation Filter*
    • Web Filtering
    • Anti-Malware
    • IPS
    • Application Patrol
    • Nebula Professional Pack
  • SecuReporter
    • 클라우드 기반 각종 보안 및 트래픽 분석
    • Daily & Weekly Report 제공
  • Hybrid VPN 지원
    • SSL
    • IPSec
    • Tailscale
  • 무선AP 컨트롤러 기능 탑재
  • Secure WiFi
  • 2FA Network Access구성
  • Device HA 무중단 구성
  • NAT 및 DHCP 기능지원
  • IPv6 지원
장비 도입 사이트
용인 디지털 산업 진흥원
Data Sheet User Guide Firmware

Overview

ZyXEL USG FLEX H 시리즈는 소규모 기업부터 중견기업에 이르는 다양한 비즈니스 환경까지 폭넓게 대응할 수 있는 차세대 방화벽 솔루션으로, AI 기반 클라우드 인텔리전스를 활용한 다중 레이어 보안과 고급 네트워크 기능을 통합한 고성능 보안 장비입니다. 새롭게 탑재된 Multi-GbE 포트는 고속ㆍ고대역폭을 요구하는 최신 네트워크 환경에 최적화되어 안정적이면서도 빠른 데이터 전송을 제공합니다. 차세대 운영체제인 uOS는 멀티 코어 CPU와 Fastpath 기술을 기반으로 한 고속 패킷 처리 구조를 통해 기존 USG FLEX 및 ATP 시리즈 대비 최대 300% 향상된 성능을 제공합니다. 또한, 직관적이고 사용자 중심의 인터페이스를 제공하여 관리 효율성과 운영 편의성을 한층 높였습니다.

USG FLEX H 시리즈는 Nebula 클라우드 관리 플랫폼과 로컬 웹 GUI를 동시에 지원하며, 스마트 동기화(Smart Sync) 기술을 통해 두 관리 환경 간의 설정을 자동으로 동기화 시킵니다. 이를 통해 관리자는 중복 작업 없이 일관된 설정을 유지할 수 있으며, 두가지 관리 환경의 장점을 동시에 활용할 수 있습니다.

Multi-GbE 인터페이스 및 PoE+ 포트 지원

USG FLEX H 시리즈는 1GbE 외에도 2.5GbE 및 10GbE를 지원하는 Multi-GbE 포트를 탑재하여 빠른 속도와 대용량 트래픽 환경에서도 네트워크 병목을 줄이고 안정적인 성능을 제공합니다. 모든 네트워크 인터페이스는 소프트웨어 정의 방식으로 구성 가능하여 WAN과 LAN 역할을 유연하게 변경할 수 있으며, 다양한 네트워크 환경에 최적화된 맞춤형 구성을 지원합니다. 또한, 30W 전력 예산을 지원하는 PoE+ 포트를 갖추고 있어, Wi-Fi AP, IP CCTV 등 PoE 기반 네트워크 장치에 별도의 전원 공급 장치 없이 직접 전원을 공급할 수 있습니다. 이를 통해 설치 시 전원 배선 작업과 장치 비용을 줄여 설치 효율성과 경제성을 동시에 향상시킬 수 있습니다. (Multi-GbE 포트 및 PoE+ 포트의 구성은 모델별로 상이합니다)
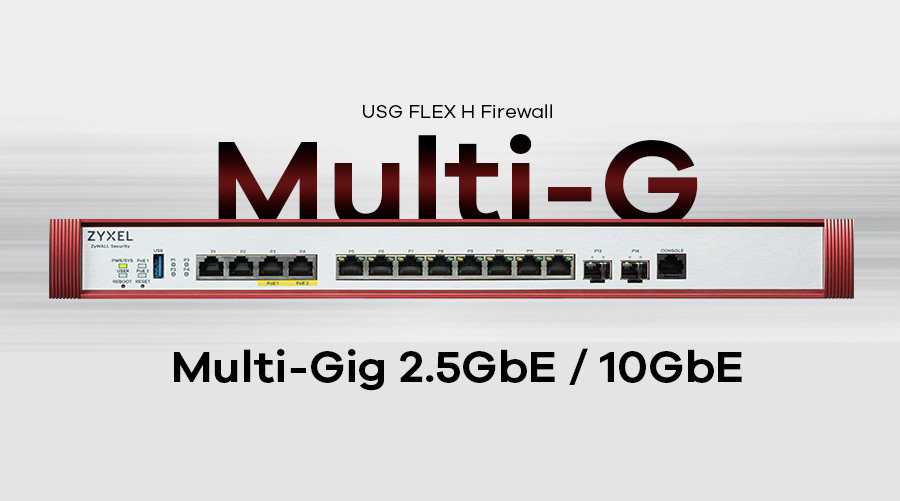
USG FLEX H Multi-GbE 인터페이스 구성도

강력하고 새로운 uOS 탑재

ZYXEL의 차세대 운영 체제인 uOS는 고속 데이터 처리와 심층 보안을 통합하여 효율적인 네트워크 운영을 제공합니다. 트래픽 위험도를 실시간 분석하고 Fast Path와 Slow Path로 자동 분기 처리해 시스템 리소스를 최적화하며 잠재적 보안 위협은 심층 검사로 대응합니다. 새롭게 설계된 GUI는 네트워크 상태, 보안 이벤트, 트래픽 흐름을 직관적인 그래픽 대시보드로 제공하여 운영자가 이상 징후나 이벤트 유형을 빠르고 간편하게 파악할 수 있도록 지원합니다. 또한, 키워드 검색, 단순화된 정책 관리, 메뉴 즐겨찾기 등록, 메뉴 검색 기능 등을 통해 설정 항목에 신속하게 접근할 수 있어 복잡한 메뉴 구조를 탐색하지 않고도 구성 변경과 실시간 모니터링이 가능해 운영 효율성을 극대화합니다.
USG FLEX H uOS 대시보드

스마트 동기화(Smart Sync)로 로컬과 클라우드 일원화 관리

기존 USG 시리즈는 로컬과 클라우드 관리 방식을 별개의 요소로 취급했으나, USG FLEX H 시리즈는 스마트 동기화(Smart Sync) 기술을 통해 두 가지 관리 방식을 동시에 사용할 수 있게 되었습니다. 보안 정책이나 네트워크 설정이 로컬 또는 클라우드에서 변경되면 자동으로 양방향 동기화가 이루어져 관리자가 중복 작업을 수행하지 않아도 설정 내용과 정책을 일관되게 유지할 수 있습니다. 이를 통해 운영자는 로컬 관리의 세밀한 제어와 클라우드 관리의 중앙 집중 모니터링, 통합 로그 분석 등 두 가지 관리 환경의 장점을 동시에 활용할 수 있습니다.
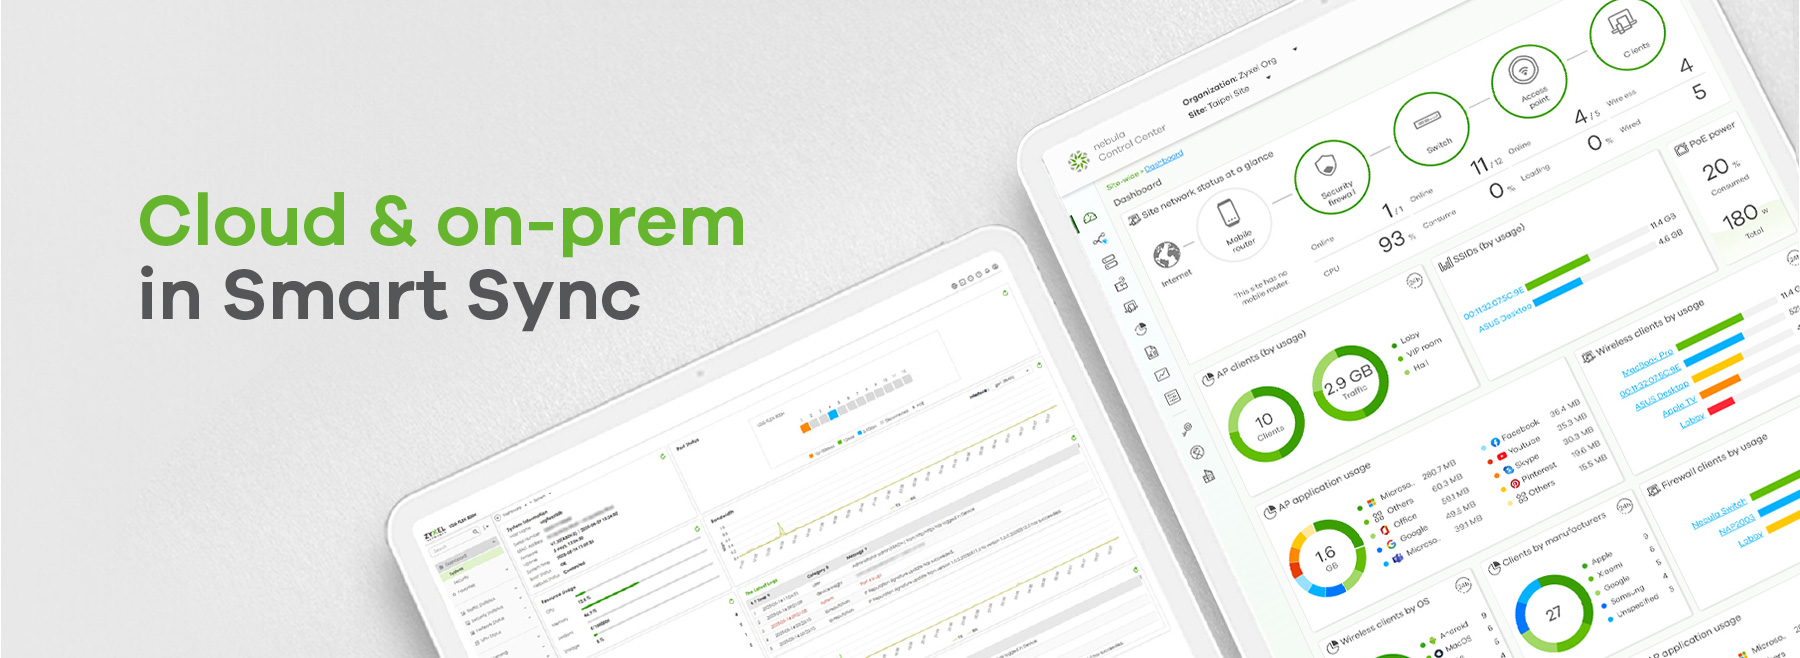
Smart Sync 로컬·클라우드 동기화 구성도

AI 기반의 클라우드 보안

USG FLEX H 시리즈는 AI 기반 클라우드 인텔리전스를 활용해 다중 레이어 보안을 제공하며 사내 네트워크를 다양한 위협으로부터 효과적으로 보호합니다. 샌드박싱, 안티 멀웨어, 앱 패트롤, DNS/IP/URL 필터링, IPS, 등 고급 보안 기능을 통합해 악성 위협을 실시간으로 탐지·차단하고, 부적절한 사용자 행동을 제한합니다. 분석된 위협 데이터는 ZYXEL 보안 클라우드에 수집 및 공유되어 전 세계의 ZYXEL 방화벽 장비가 동일한 위협을 신속하게 인식하고 대응할 수 있도록 지원합니다. 또한, 지속적인 보안 시그니처 업데이트를 통해 알려진 위협뿐 아니라 제로데이 공격에도 즉각적인 대응이 가능합니다.

VPN 솔루션

Zyxel VPN 솔루션은 본사와 지사, 원격 근무자 간 안전한 연결을 위한 네트워크 보안 솔루션입니다. Site-to-Site VPN은 고비용 전용 회선을 대체해 본사와 지사를 하나의 네트워크처럼 연결하고, Remote Access VPN은 재택근무자나 출장 중인 직원이 언제 어디서나 안전하게 사내 네트워크에 접속할 수 있도록 지원합니다. 특히 Zyxel 전용 유틸리티인 SecuExtender VPN Client와 운영체제별 프로비저닝 스크립트는 복잡한 VPN 설정 과정을 간소화하여 IT 관리자와 사용자 모두에게 높은 편의성을 제공합니다. 또한, WireGuard 기반의 Tailscale과의 연동을 통해 NAT 환경에서도 별도의 복잡한 설정 없이 안정적인 VPN 연결을 구현할 수 있습니다.

USG FLEX H VPN 솔루션 구성도

무선AP 컨트롤러 기능 APC(AP Controller) 탑재

USG FLEX H 시리즈는 무선 AP 컨트롤러 기능을 내장하고 있어, 사내 유무선 네트워크를 통합적으로 관리할 수 있습니다. 별도의 물리적 컨트롤러 없이도 무선 환경을 구축할 수 있어 초기 비용을 절감할 수 있으며, 설치된 무선 AP의 관리, 무선 환경 구성, 사용자 접속 인증, 보안 설정, 무선 네트워크 모니터링 등을 중앙에서 효율적으로 수행할 수 있습니다. 기본적으로 8대의 AP를 관리할 수 있으며, 라이선스를 추가하면 최대 520대까지 관리가 가능하므로 중소규모 사무실, 병원, 학교 등 무선 네트워크의 보안과 관리가 동시에 필요한 환경에 최적화된 무선 보안 솔루션을 제공합니다. (AP 기본 관리 수량은 8대이며, 최대 관리 가능 AP 대수는 모델별로 상이합니다)
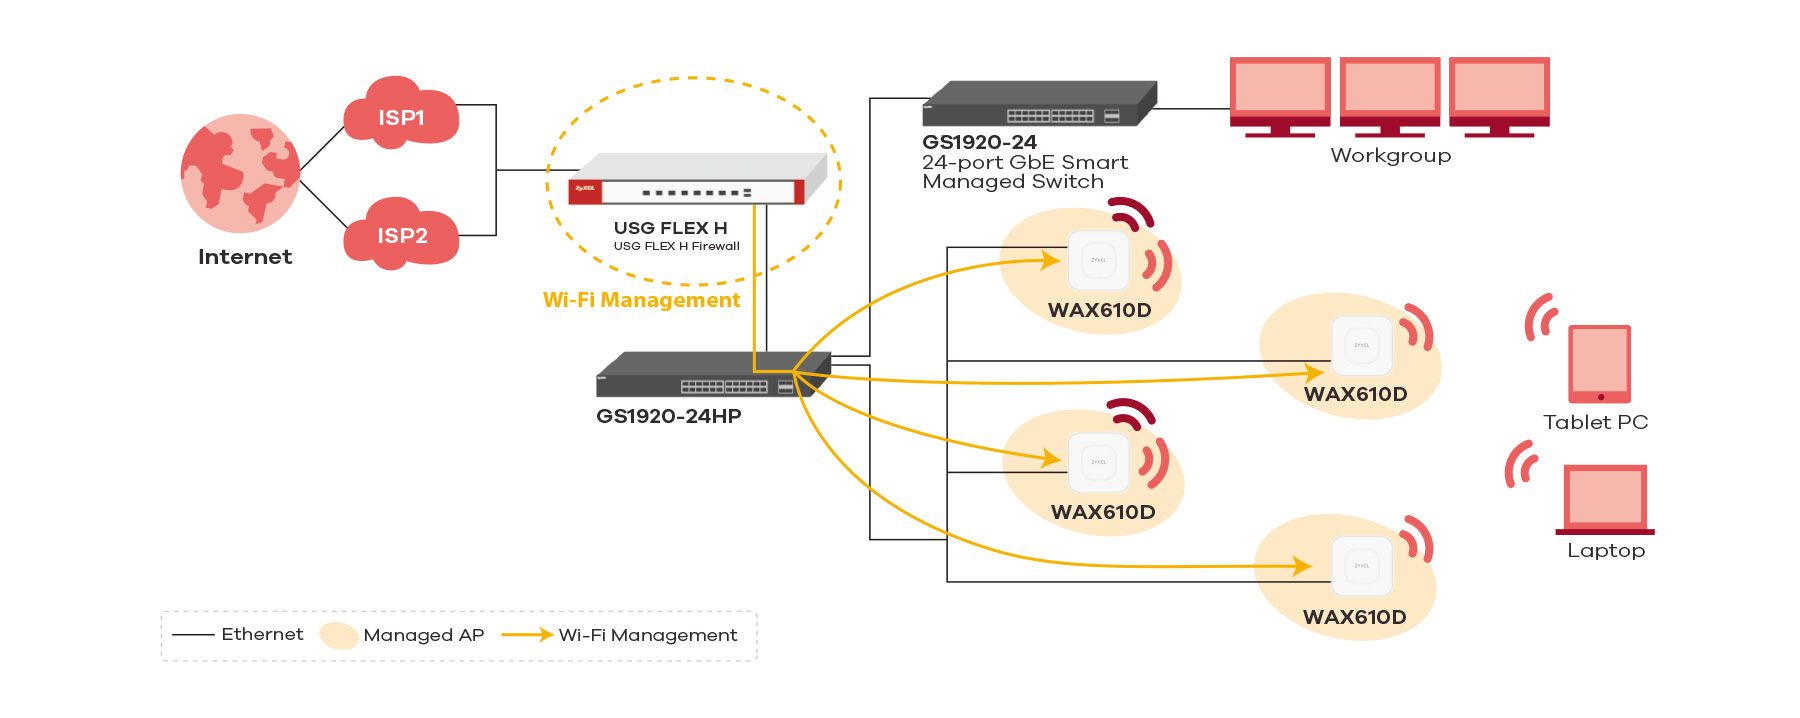
AP Controller 관리 화면

SecuReporter

SecuReporter는 클라우드 기반의 지능형 보안 분석 리포트 서비스로 ZYXEL USG FLEX H에서 실시간 수집된 로그와 트래픽 데이터를 통합 분석하여 네트워크 보안 현황을 한눈에 확인할 수 있도록 지원합니다. 대시보드 화면에서 위협 발생 지점, 트래픽 영향, 탐지 현황 등을 직관적으로 파악할 수 있으며, 여러 보안 장비의 로그를 한곳에서 분석해 위협을 쉽게 찾아내고 연관성까지 분석할 수 있습니다. 또한, 다차원 분석이 가능하여 단순 차단 로그를 넘어 누가, 언제, 어떤 디바이스로, 어떤 앱이나 웹을 통해 위협에 노출되었는지까지 세부적으로 확인할 수 있으며, AI SecuPilot 기능을 이용하면 AI 어시스턴트에게 직접 질문하여 복잡한 위협 분석을 보다 쉽고 빠르게 수행할 수 있습니다. 수집된 분석 결과는 일간·주간 단위의 PDF 보고서로 제공되어 보안 현황을 체계적으로 관리할 수 있으며, 클라우드 인프라를 활용하므로 별도의 분석 서버나 저장 공간이 필요하지 않아 보안운영센터나 중대형 네트워크 환경에 특히 유용합니다.
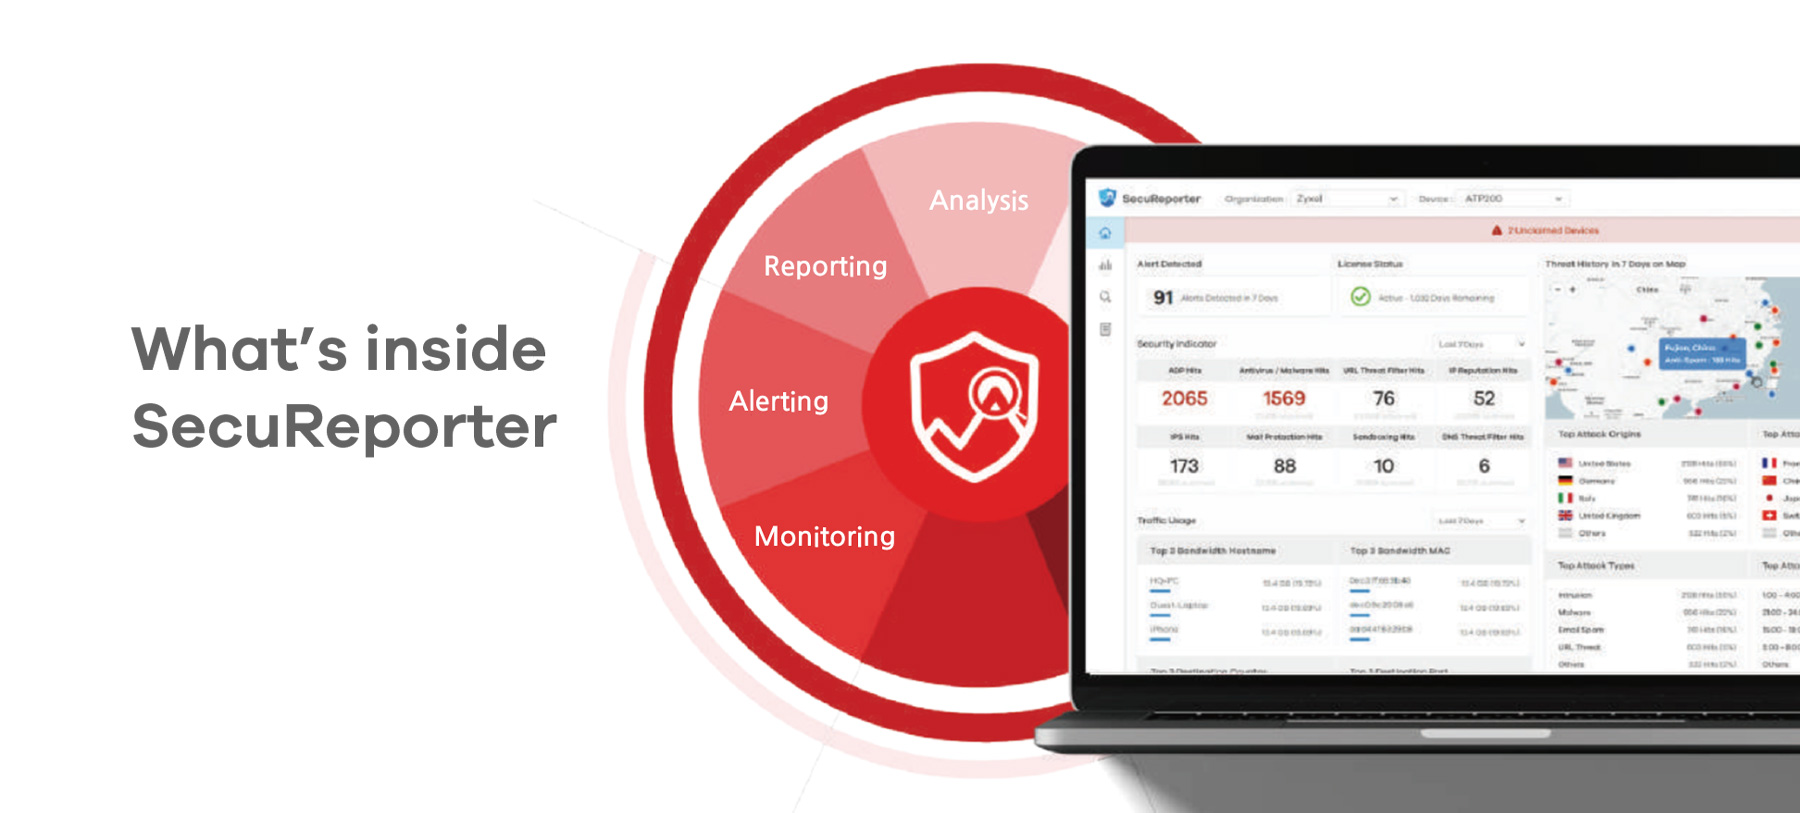
SecuReporter 보안 분석 대시보드
Model USG FLEX 100H USG FLEX 200H
Product photo USG FLEX 100H USG FLEX 200H
Hardware Specifications
Network Interfaces100M/1G Ethernet (RJ-45)86
100M/1G/2.5G Ethernet (RJ-45)-2
1G/2.5G/5G/10G Ethernet (RJ-45)--
1G SFP/10G SFP+--
USB 3.0 Type-A11
Console portYes (RJ-45)Yes (RJ-45)
Rack-mountable-Yes
FanlessYesYes
System Capacity & Performance*1
SPI firewall throughput (Mbps)*24,0006,500
VPN throughput (Mbps)*39001,200
IPS throughput (Mbps)*41,5002,500
Anti-Malware throughput (Mbps)*41,0001,800
UTM throughput (Anti-Malware and IPS)*41,0001,800
Max. TCP concurrent sessions*5300,000600,000
Max. concurrent IPSec VPN tunnels*650100
Recommended gateway-to-gateway IPSec VPN tunnels2050
Concurrent SSL VPN users2550
VLAN interface1632
Speedtest Performance
SPI firewall throughput (Mbps)*7931.61929.97
Key Features
Security Service*8Anti-MalwareYesYes
IPSYesYes
Application PatrolYesYes
Web FilteringYesYes
Reputation FilterYesYes
SecuReporterYesYes
SandboxingYesYes
Security Profile SyncYesYes
Device InsightYesYes
SSL (HTTPS) InspectionYesYes
Two-Factor AuthenticationYesYes
SD-WAN & VPNWAN load balancingYesYes
Prioritize critical applicationsYesYes
VPNVPN ProtocolIKEv2/IPSec, SSL, Tailscale*9IKEv2/IPSec, SSL, Tailscale*9
Nebula SD-VPNYesYes
Auto-link VPNYesYes
Manual-link VPNYesYes
VPN TopologyYesYes
WLAN ManagementDefault Number of Managed AP88
Secure WiFi*8YesYes
Maximum Number of Tunnel-Mode AP*10610
Maximum Number of Managed AP2440
Recommend max. AP in 1 AP Group1020
Management & ConnectivityNebula Centralized ManagementYesYes
Device HA-Yes
Link Aggregation (LAG)YesYes
Concurrent devices logins (max.)*1164200
Burst login rate (users/30sec)64200
Power Requirements
Power input12V DC, 2A max.12V DC, 2A max.
Max. power consumption (Watt max.)100H: 17 / 100HP: 51.2200H: 22 / 200HP: 62
Heat dissipation (BTU/hr)40.36558.75
Physical Specifications
ItemDimensions (WxDxH) (mm/in.)216 x 143 x 33 / 8.50 x 5.63 x 1.30272 x 187 x 36 / 10.7 x 7.36 x 1.42
Weight (kg/lb.)1.04 / 2.291.52 / 3.34
PackingDimensions (WxDxH) (mm/in.)278 x 189 x 99 / 10.94 x 7.44 x 3.89427 x 247 x 73 / 16.81 x 9.72 x 2.87
Weight (kg/lb.)1.62 / 3.572.43 / 5.36
Included accessories• Power adapter
• RJ-45 to RS-232 cable for console connection
• Power adapter
• RJ-45 to RS-232 cable for console connection
• Rack mounting kit (optional, by regions)
Environmental Specifications
OperatingTemperature0°C to 40°C / 32°F to 104°F0°C to 40°C / 32°F to 104°F
Humidity10% to 90% (non-condensing)10% to 90% (non-condensing)
StorageTemperature-30°C to 70°C / -22°F to 158°F-30°C to 70°C / -22°F to 158°F
Humidity10% to 90% (non-condensing)10% to 90% (non-condensing)
MTBF (hr)40°C / 353878.1057 hr
25°C / 602150.9604 hr
40°C / 306768.409 hr
25°C / 528037.0106 hr
Acoustic noise--
Certifications
EMCFCC Part 15 (Class B), CE EMC (Class B), RCM (Class B), BSMIFCC Part 15 (Class B), CE EMC (Class B), RCM (Class B), BSMI
SafetyLVD (EN62368-1), BSMILVD (EN62368-1), BSMI
*: This matrix with firmware uOS1.36 or later.
*1: Actual performance may vary depending on system configuration, network conditions, and activated applications.
*2: Maximum throughput based on RFC 2544 (1,518-byte UDP packets).
*3: VPN throughput measurements are based on RFC2544 (1,424-byte UDP packets).
*4: Anti-Malware (with Express Mode) and IPS throughput is measured using the industry standard HTTP performance test (1,460-byte HTTP packets). Testing done with multiple flows.
*5: Maximum sessions are measured using the industry standard IXIA IxLoad testing tool.
*6: Including Gateway-to-Gateway and Client-to-Gateway.
*7: The Speedtest result is conducted with 1Gbps WAN link in real world and it is subject to fluctuate due to quality of the ISP link.
*8: Requires a Zyxel service license to enable or extend feature capacity. SSL (HTTPS) inspection and Two-Factor Authentication are default supported features for any registered USG FLEX H device.
*9: Local GUI only.
*10: Available in Q3, 2026.
*11: This is the recommended maximum number of concurrent logged-in devices.
Anti-Malware 아이콘

Anti-Malware

클라우드 기반 최신 악성코드 데이터베이스와 파일 해시 비교를 통해 바이러스, 웜 등 알려진 악성 파일을 차단
Web Filtering 아이콘

Web Filtering

클라우드 기반 웹 평판 데이터베이스를 활용해 악성·유해 웹사이트 및 업무 무관 컨텐츠 접근을 차단
Sandboxing 아이콘

Sandboxing

알려지지 않은 파일을 클라우드 가상 환경에서 격리·분석하여 신종 악성코드와 제로데이 공격에 효과적으로 대응
Reputation Filter 아이콘

Reputation Filter

최신 클라우드 평판 데이터베이스를 기반으로 IP, 도메인, URL의 신뢰도를 검증하고 악성으로 판정된 사이트에 대한 접근을 차단
IPS 아이콘

IPS

DPI 엔진을 통해 네트워크 및 애플리케이션 계층의 취약점을 악용한 공격 시도나 비정상적인 트래픽 패턴을 감지하여 위협을 차단
Application Patrol 아이콘

Application Patrol

수천 개의 애플리케이션을 자동으로 식별·분류하여 우선순위 지정, 대역폭 관리, 차단까지 다양한 트래픽 제어 모드 지원
SecuReporter 아이콘

SecuReporter

중앙 대시보드와 맞춤형 리포트를 통해 네트워크 현황과 보안 이벤트를 한눈에 파악하고 신속하게 대응 가능
Secure Wi-Fi 아이콘

Secure Wi-Fi

AP 관리 용량을 최대로 확장할 수 있어 대규모 무선 AP 환경도 중앙에서 통합 관리

Security Service

Firewall

  • Routing and transparent (bridge) modes
  • Stateful packet inspection
  • Source IP Spoofing Prevention
  • FTP ALG/SIP Pinhole
  • Dos Prevention (Preventing Flood and Sweep Attacks)
  • Per host session limit
  • Support External IP Block List
  • Flooding detection and protection

Security Policy

  • Unified policy management interface
  • Support Content Filtering, Application Patrol, firewall (ACL)
  • Firewall: SSL inspection
  • Policy criteria: source and destination IP address, user group, time
  • Policy criteria: zone, user

Intrusion Prevention System (IPS)

  • Streamed-based engine
  • Signature-based scanning
  • Support both intrusion detection and prevention
  • Support allow list (whitelist) to deal with false positives involving known benign activity
  • Support exploit-based and vulnerability-based protection
  • Support Web attacks like XSS and SQL injection
  • Automatic new signature update mechanism support

Application Patrol

  • Smart single-pass scanning engine
  • Identifies and control thousands of applications and their behaviors
  • Support more than 50 application categories
  • GenAI App Visibility & Control
  • Granular control over the most popular applications
  • Real-time application statistics and reports
  • Identify and control the use of DoH (DNS over HTTPS)

Anti-Malware

  • High performance query-based scan engine (Express Mode)
  • Works with over 30 billion of known malicious file identifiers and still growing
  • Wild range file type examination
  • Support HTTP/SMTP/POP3/FTP scan

Sandboxing

  • Cloud-based multi-engine inspection
  • Support HTTP/SMTP/POP3/FTP scan
  • Wild range file type examination
  • Real-time threat synchronization

IP Reputation Filter

  • IP-based reputation filter
  • Supports 9 Cyber Threat Categories
  • Inbound & Outbound traffic filtering
  • Support Block and Allow List

DNS Threat Filter

  • Block clients to access malicious domain
  • Block and Allow List support
  • Monitoring or blocking the use of DoH/DoT

URL Threat Filter

  • Botnet C&C websites blocking
  • Malicious URL blocking
  • Support Block and Allow List

External Block List

  • Importing malicious IP/URL from external sources
  • Works with IP Reputation and URL Threat Filter

Web Filtering

  • HTTPs domain filtering
  • DNS domain filtering
  • Allow List websites enforcement
  • Customizable warning messages and redirect URL
  • URL categories increased to 111
  • CTIRU (Counter-Terrorism Internet Referral Unit) support
  • Support Block and Allow List
  • DNS SafeSearch

SSL Inspection

  • Deep packet inspection for TLS
  • Support inspect TLS1.3
  • Support untrusted certificate blocking
  • Works with IPS/Anti-Malware/Sandboxing/Application Patrol/Web Filtering

Device Insight

  • Agentless Scanning for discovery and classification of devices
  • View all devices on the network, including wired, wireless, BYOD, IoT, and SecuExtender (remote endpoint) on SecuReporter
  • Visibility of network devices (switches, wireless access points, firewalls) from Zyxel or 3rd party vendors
  • Visibility of networks devices from Astra Client

Geo Enforcer

  • Geo IP blocking
  • Geographical visibility on logs

IP Exception

  • Provides granular control for target source and destination IP
  • Supports security service scan bypass for IPS, Anti-Malware and URL Threat Filter

VPN

IPSec VPN

  • Route-based and Policy-based Site to Site
  • Client remote access (IKEv2 MS-CHAPv2)
  • IKEv2 (EAP, configuration payload)
  • Encryption: DES, 3DES, AES (256-bit)
  • Authentication: MD5, SHA1, SHA2 (512-bit)
  • Perfect forward secrecy (DH groups) support 2, 5, 14-16, 19-21, 28-30
  • PSK and PKI (X.509) certificate authentication
  • IPSec NAT traversal (NAT-T)
  • Dead Peer Detection (DPD) and relay detection
  • NAT over IPSec
  • SecuExtender VPN Client provision
  • Support native Windows, iOS/macOS and Android (StrongSwan) client provision
  • Support 2FA Google Authenticator/Microsoft Authenticator

SSL VPN

  • Client remote access*
  • Full/Split tunnel mode
  • SecuExtender VPN client provision
  • Support 2FA Google Authenticator/Microsoft Authenticator

Tailscale VPN*2

  • Mesh-capable VPN
  • Supports native identity providers, including Google, Microsoft Entra ID, Apple ID, etc.
  • Supports Windows, Linux, Android, and iOS agents

Networking

Connection

  • Routing/Transparent mode
  • Ethernet and PPPoE
  • NAT and PAT
  • VLAN tagging (802.1Q)
  • Static route
  • Policy-based routing (user-aware)
  • Policy-based NAT (SNAT)
  • IGMP Proxy
  • DHCP client/server/relay
  • Dynamic DNS support
  • Multi-WAN load balancing/failover (Round Robin, LLF, Split over)
  • Bandwidth Management
  • Link Aggregation support (LAG)

WLAN Management*2

  • Supports AP Controller (APC)
  • WPA3 support on 802.11ax AP
  • WPA2 Enterprise (802.1x)
  • 802.11r/k/v support
  • Support auto AP firmware update
  • Dynamic Channel Selection (DCS)
  • Band steering (Band select)
  • Wireless L2 Isolation
  • CAPWAP discovery method
  • Multiple SSID with VLAN
  • Support Multi-Link Operation (MLO)
  • Support AP Load Balancing
  • Support MAC Filtering (Block/Allow)
  • Supports Smart Mesh

Management

Nebula Centralized Management

  • Centralized device, client, and application usage monitoring (logs and statistics)
  • On-premises settings in Nebula
  • Cloud & on-prem security integrated with smart sync
  • Security Profile Sync
  • Nebula SD-VPN
  • Auto-link VPN
  • Manual-link VPN
  • VPN Topology
  • Monitor device on/off status
  • Keep event log up to 1 year
  • Firmware upgrading operation
  • Remote SSH for accessing device GUI
  • Backup and restore firewall configurations (requires Nebula Pro Pack)

SD-WAN

  • Orchestration of secure connections across multiple locations
  • Supporting mesh or hub-and-spoke topology
  • Prioritizing mission-critical applications
  • High availability and failover

Authentication

  • Local user database
  • External user database
  • IKEv2 with EAP-MSCHAPv2 VPN authentication
  • Supports 2FA authentication (Google Authenticator, Microsoft Authenticator)
  • 802.1x Authentication
  • Captive Portal Web Authentication

System Management

  • Multi-lingual Web GUI (HTTPS and HTTP)
  • Command line interface (console, SSH)
  • SNMP v1, v2c, v3
  • System configuration rollback
  • Configuration auto backup
  • Recovery Manager (one-click full backup of configuration, certificates)
  • Firmware upgrade via FTP, FTP-TLS
  • Firmware upgrade via Web GUI
  • New firmware notifications and auto upgrade
  • Dual firmware images

Logging and Monitoring

  • Comprehensive local logging
  • Syslog (to up to 4 servers*1)
  • Event Notification and Email alerts
  • Real-time traffic monitoring
  • Built-in daily report
  • SecuReporter supported

External Integration

Tailscale VPN*2

  • Mesh-capable VPN
  • Supports native identity providers, including Google, Microsoft Entra ID, Apple ID, etc.
  • Supports Windows, Linux, Android, and iOS agents

Avast SMB*3

  • Online management platform
  • Endpoint Protection
  • Ransomware & Data Protection
  • Phishing Protection
  • Web Control
  • Personal VPN
  • USB Protection
  • Patch Management

*: Compatible with OpenVPN Connect
*1: Up to 4 servers via CLI, default 2 servers
*2: Local GUI only
*3: Requires an active Avast license. Features listed are provided and managed by Avast.

USG FLEX H 시리즈는 아래 AP 모델에 한해 APC 기능을 지원합니다.

Series Model Supported Managed APs
USG FLEX H USG FLEX 100H
USG FLEX 200H
USG FLEX 500H
USG FLEX 700H
수상 및 미디어 로고
자이젤코리아
전문 엔지니어와 상담하세요.

네트워크 전문 엔지니어가
직접 확인 후 답변드립니다.

문의하기 제품 찾기